Data Policy
- Data Policy currently supports only string types
- Once encrypted data is saved as a Materialized View, it can no longer be decrypted back to plaintext
- Although Canner supports decryption, we recommend not encrypting the same column multiple times
Apply a Data Policy
Data Policies must first be configured by the Admin (see Chapter 2.8 System Administration & Settings), after which they can be applied in data sources or workspaces. Columns with a Data Policy applied are privacy-protected, and the protection also applies to any data derived from or shared from that dataset.
Step 1: Apply a Data Policy
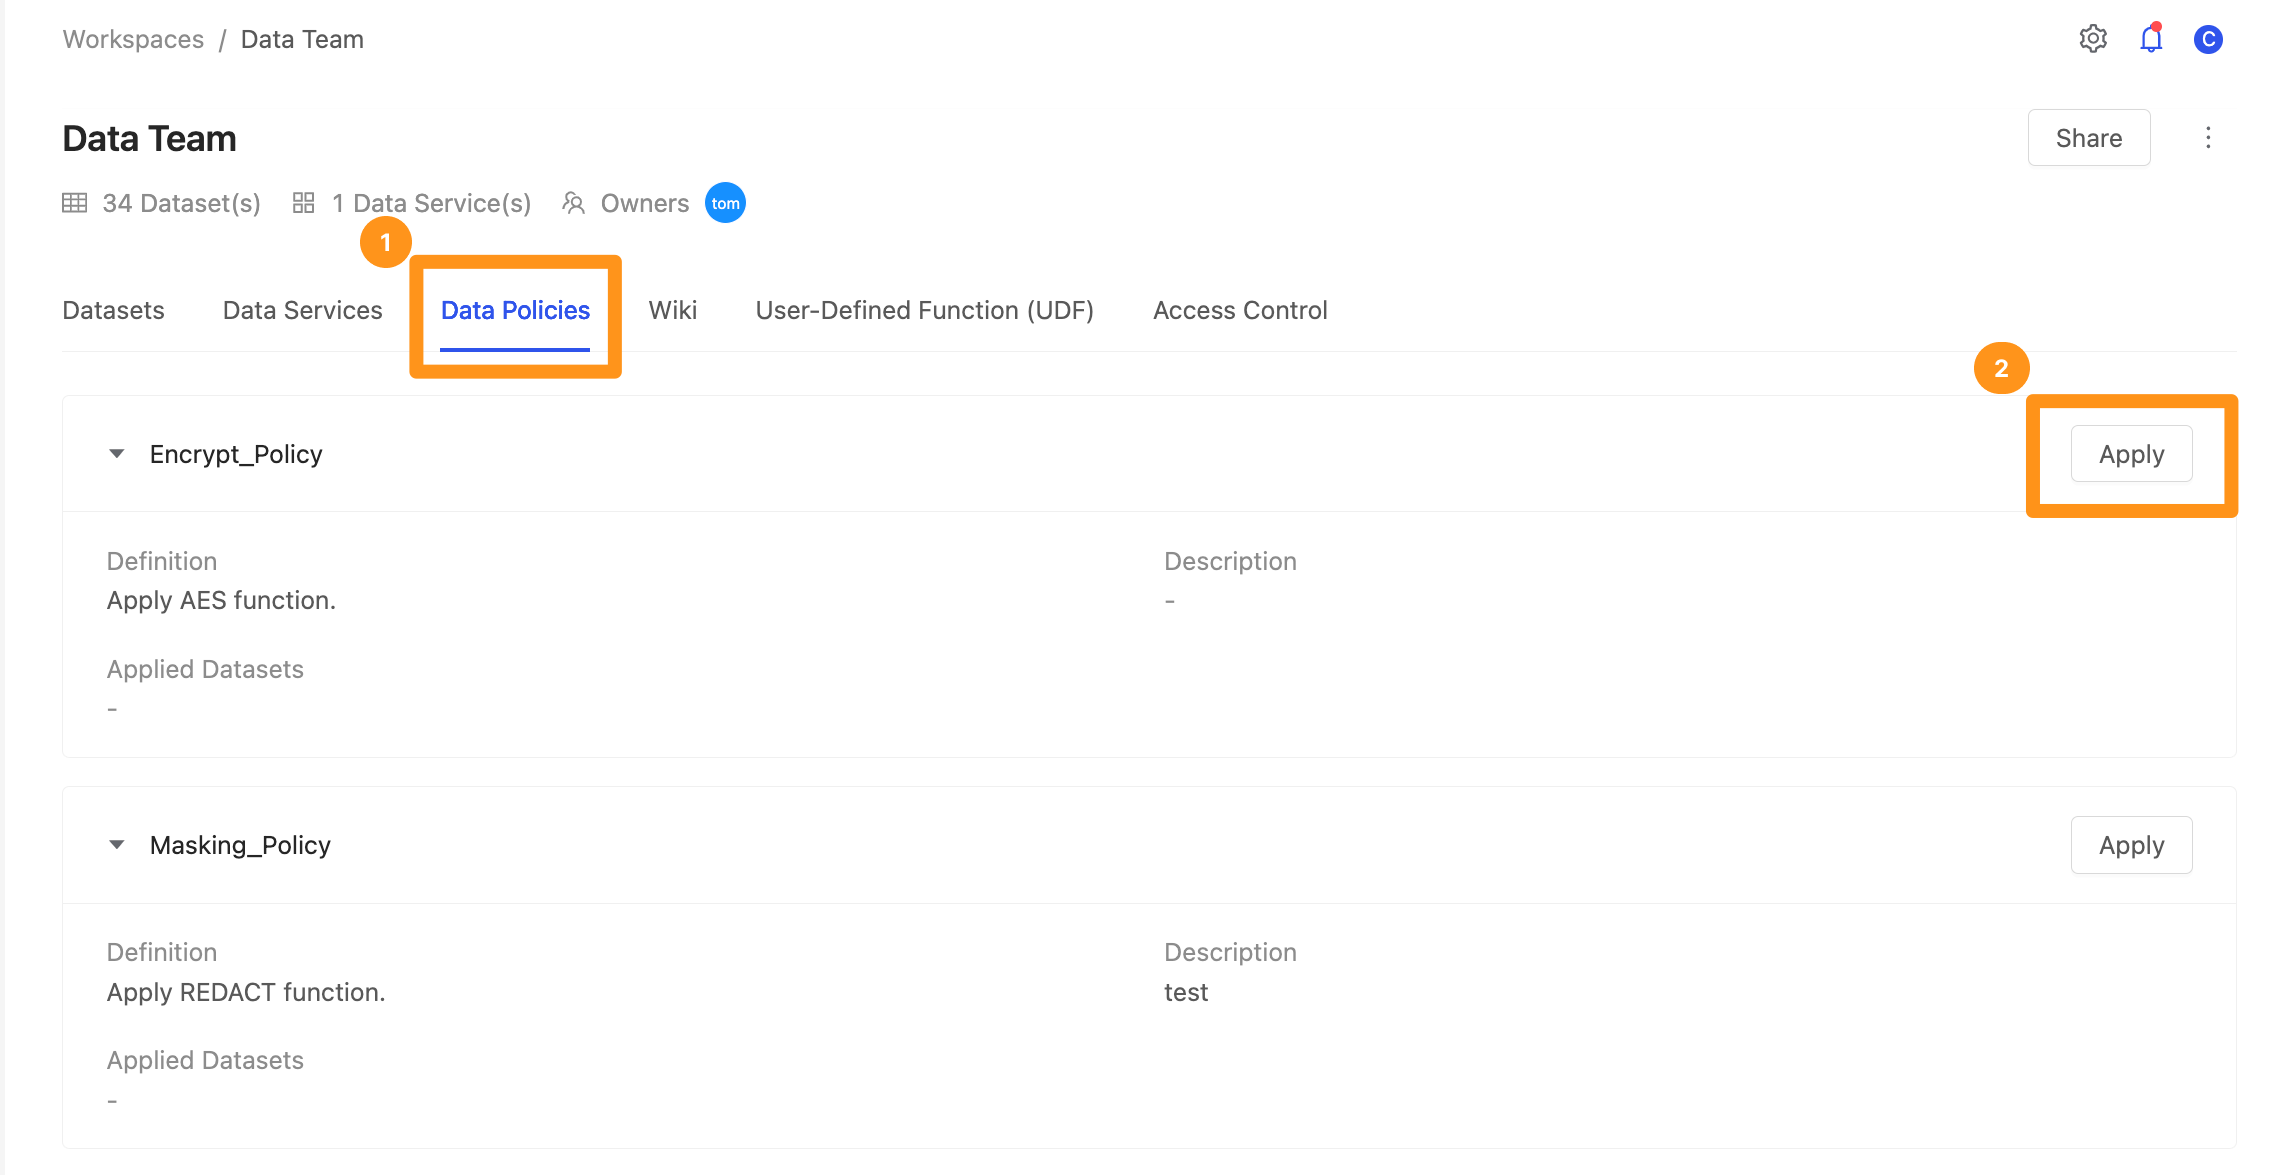
Go to the Data Policies tab of the workspace and click the Apply button to the right of a Data Policy to apply it.
This feature requires the workspace Owner to grant the Apply Data Policy permission to the user in Workspace Access Control.
-
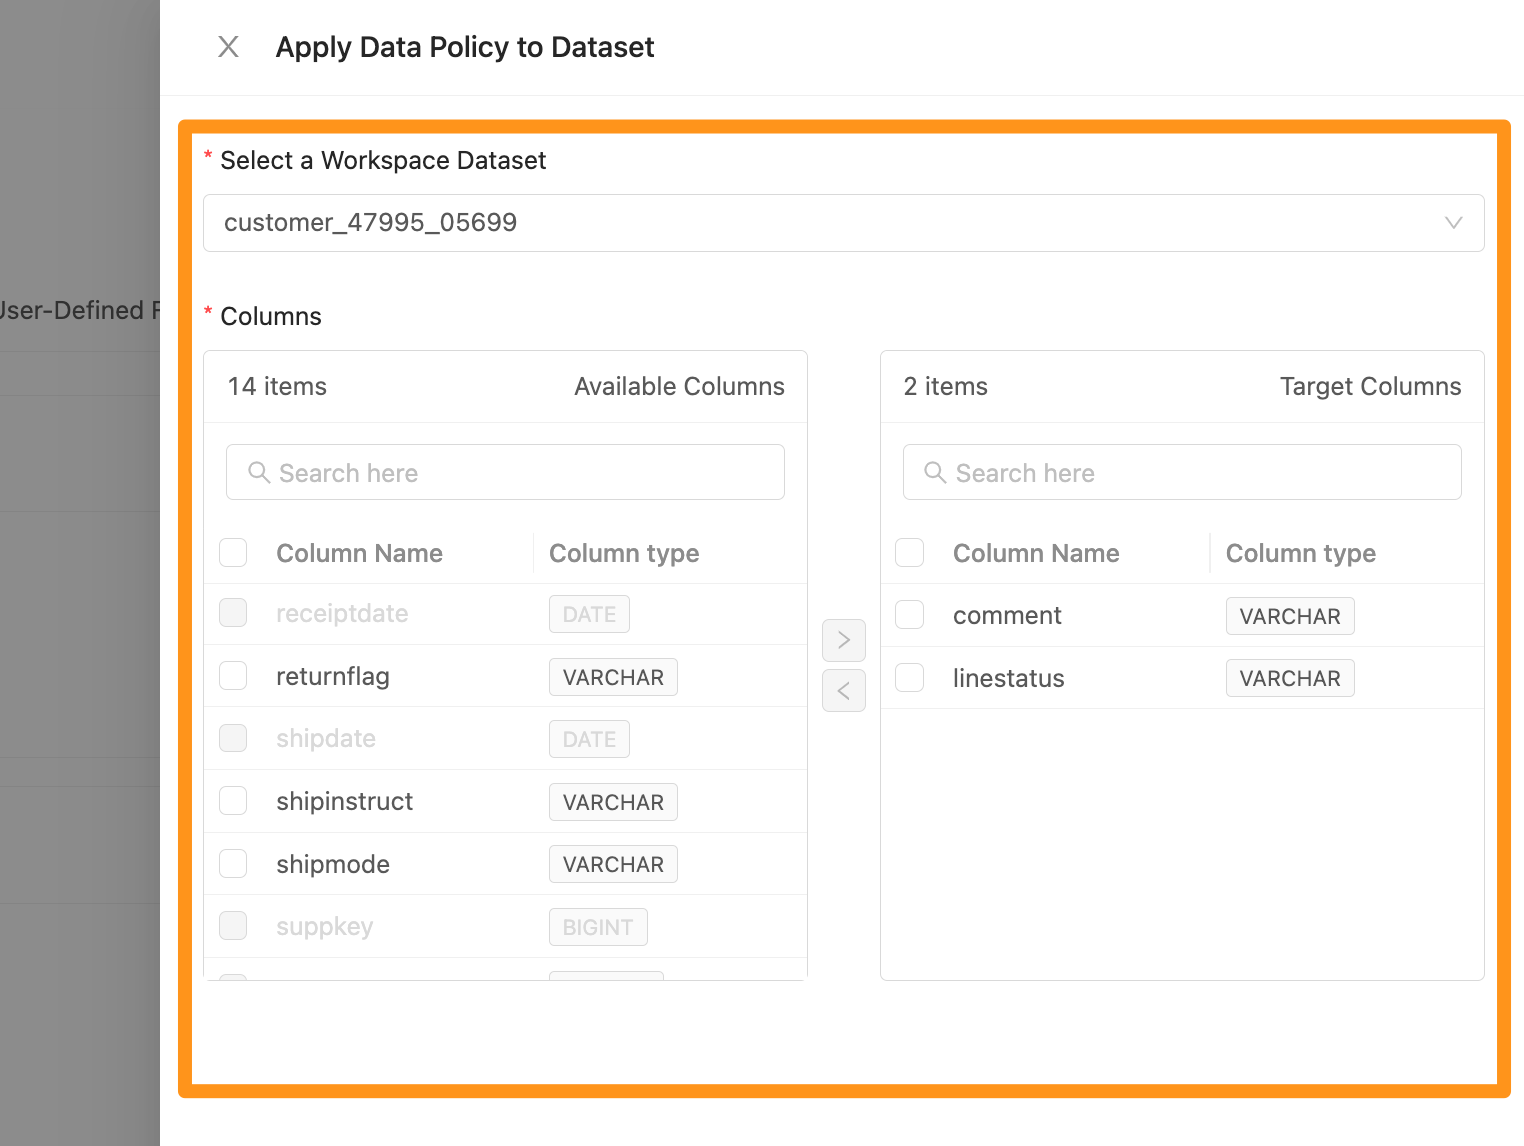
Select a Workspace Dataset: Select the dataset to apply it to
-
Columns: Select the columns to apply it to
Step 2: Finish
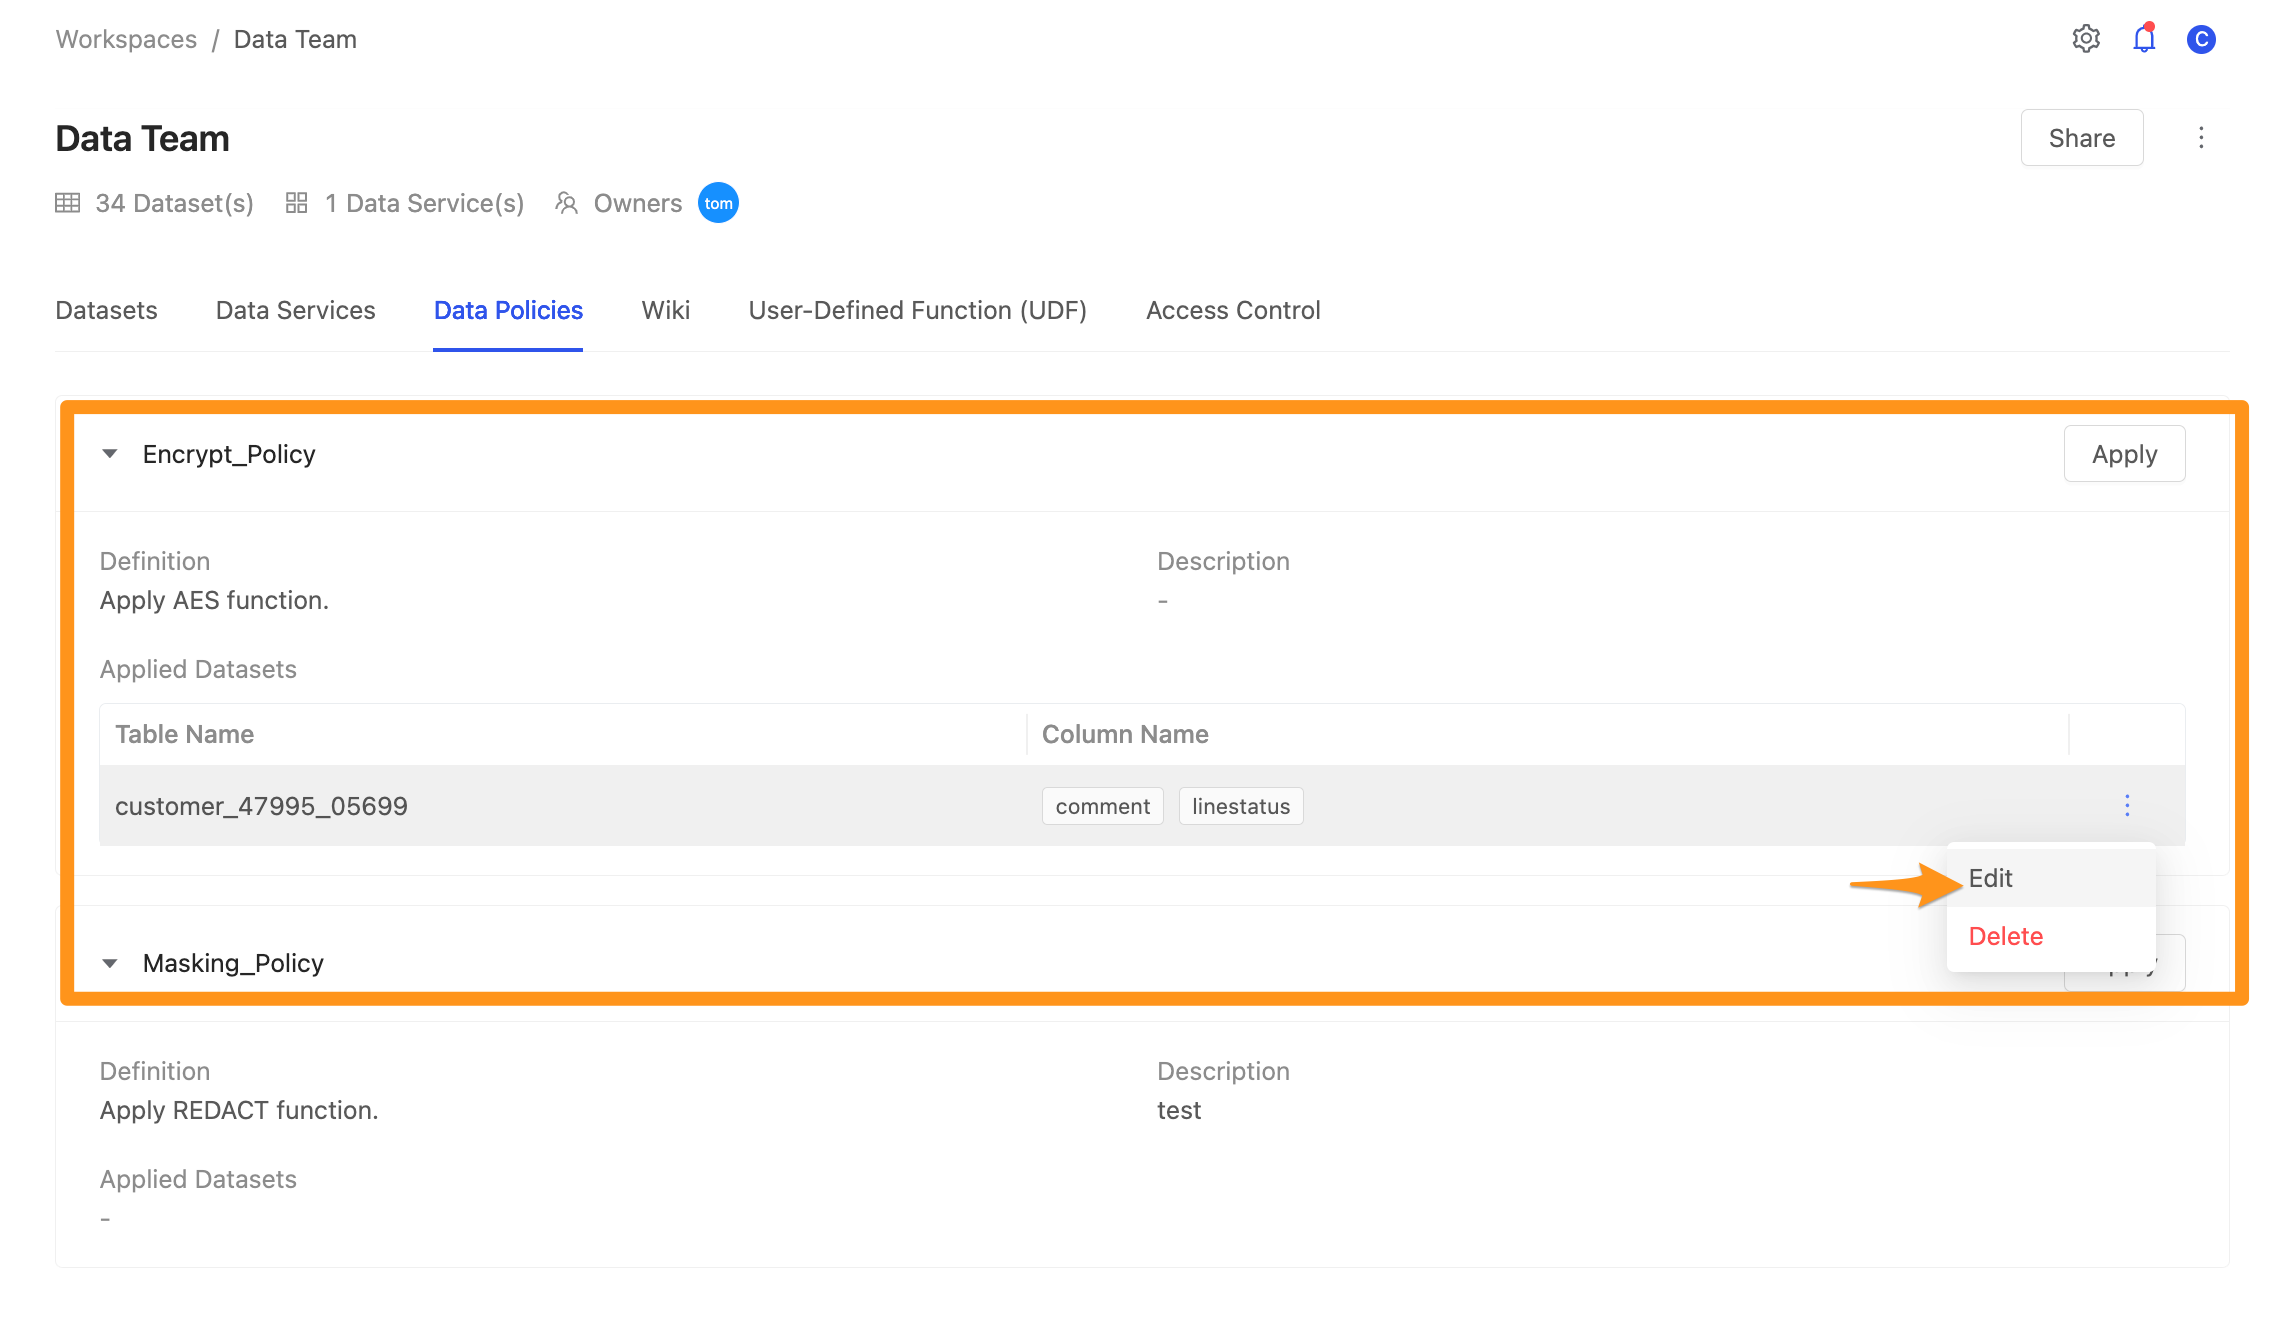
After you click Submit, you can see which datasets and columns the Data Policy is currently applied to. Click the More icon to edit or remove the applied columns.
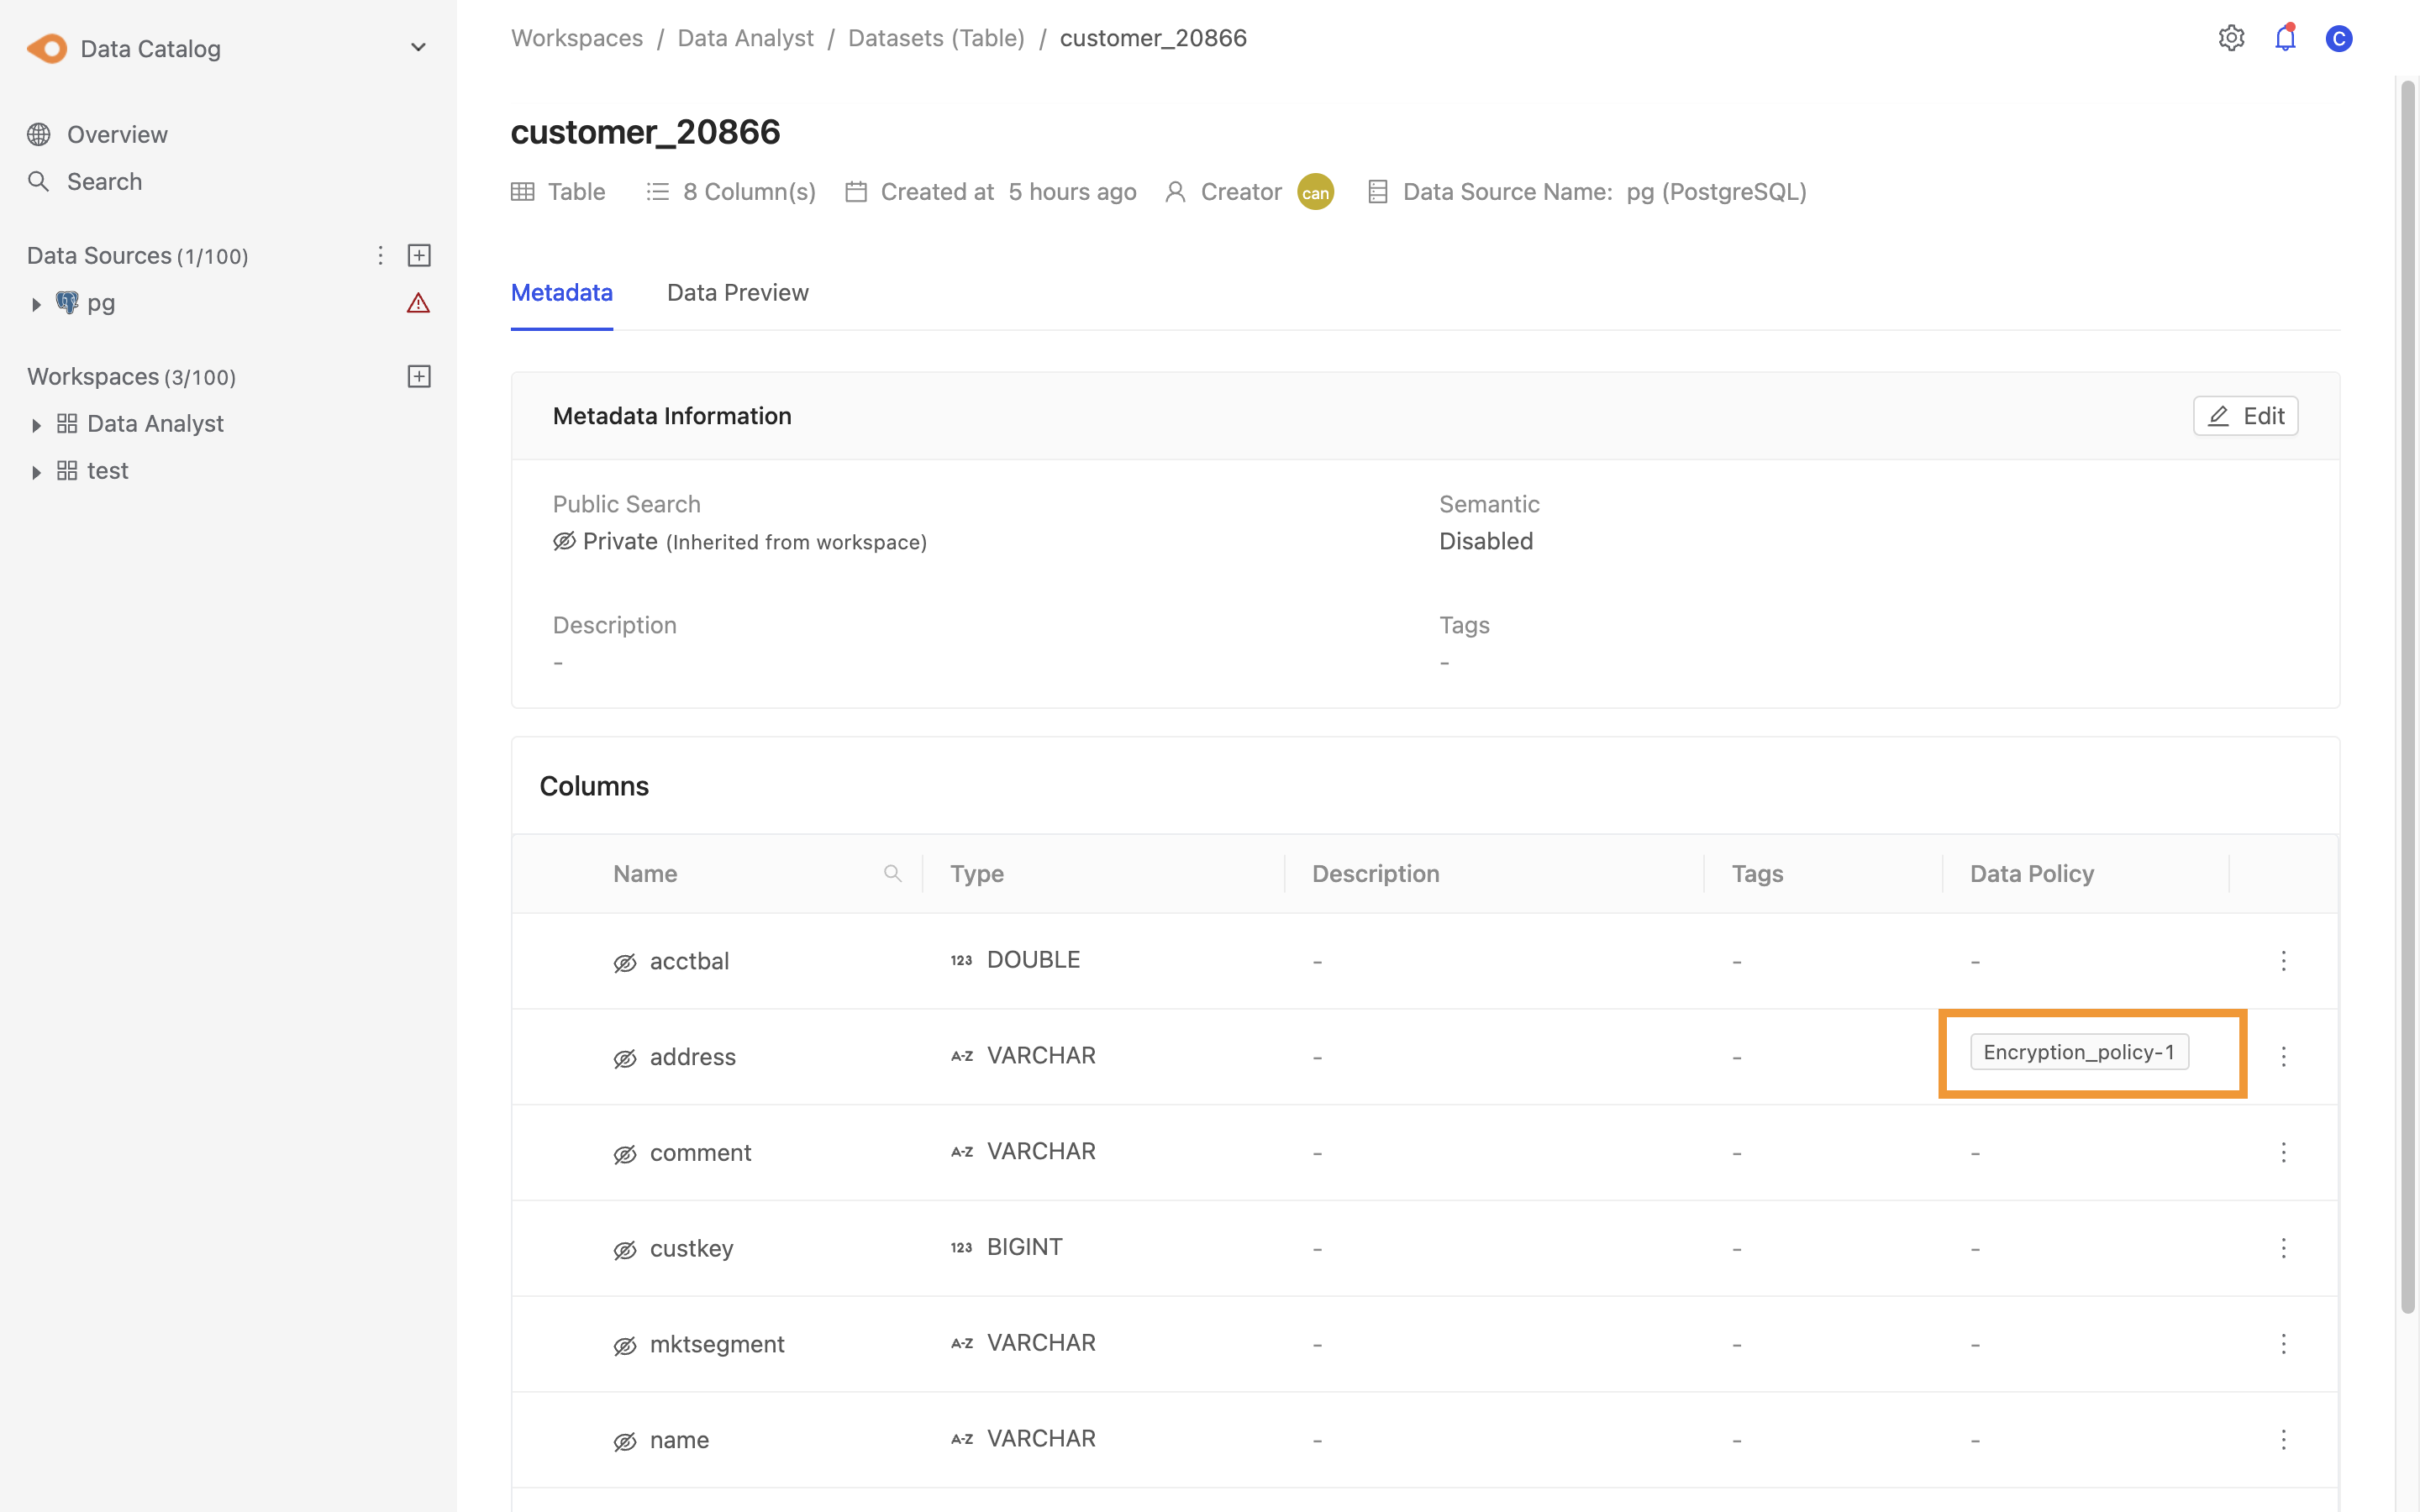
On the dataset details page in the workspace, the Metadata tab shows which columns have a Data Policy applied. If the policy was not applied on the current dataset itself, the Data Policy label is not shown, but the data is still privacy-protected. (For example, if a dataset with a Data Policy applied is shared to another workspace, the Data Policy label is not shown in that workspace, but the data is still protected.)
Decrypt data (after applying an Encryption policy)
Decryption can only be used within the Canner platform
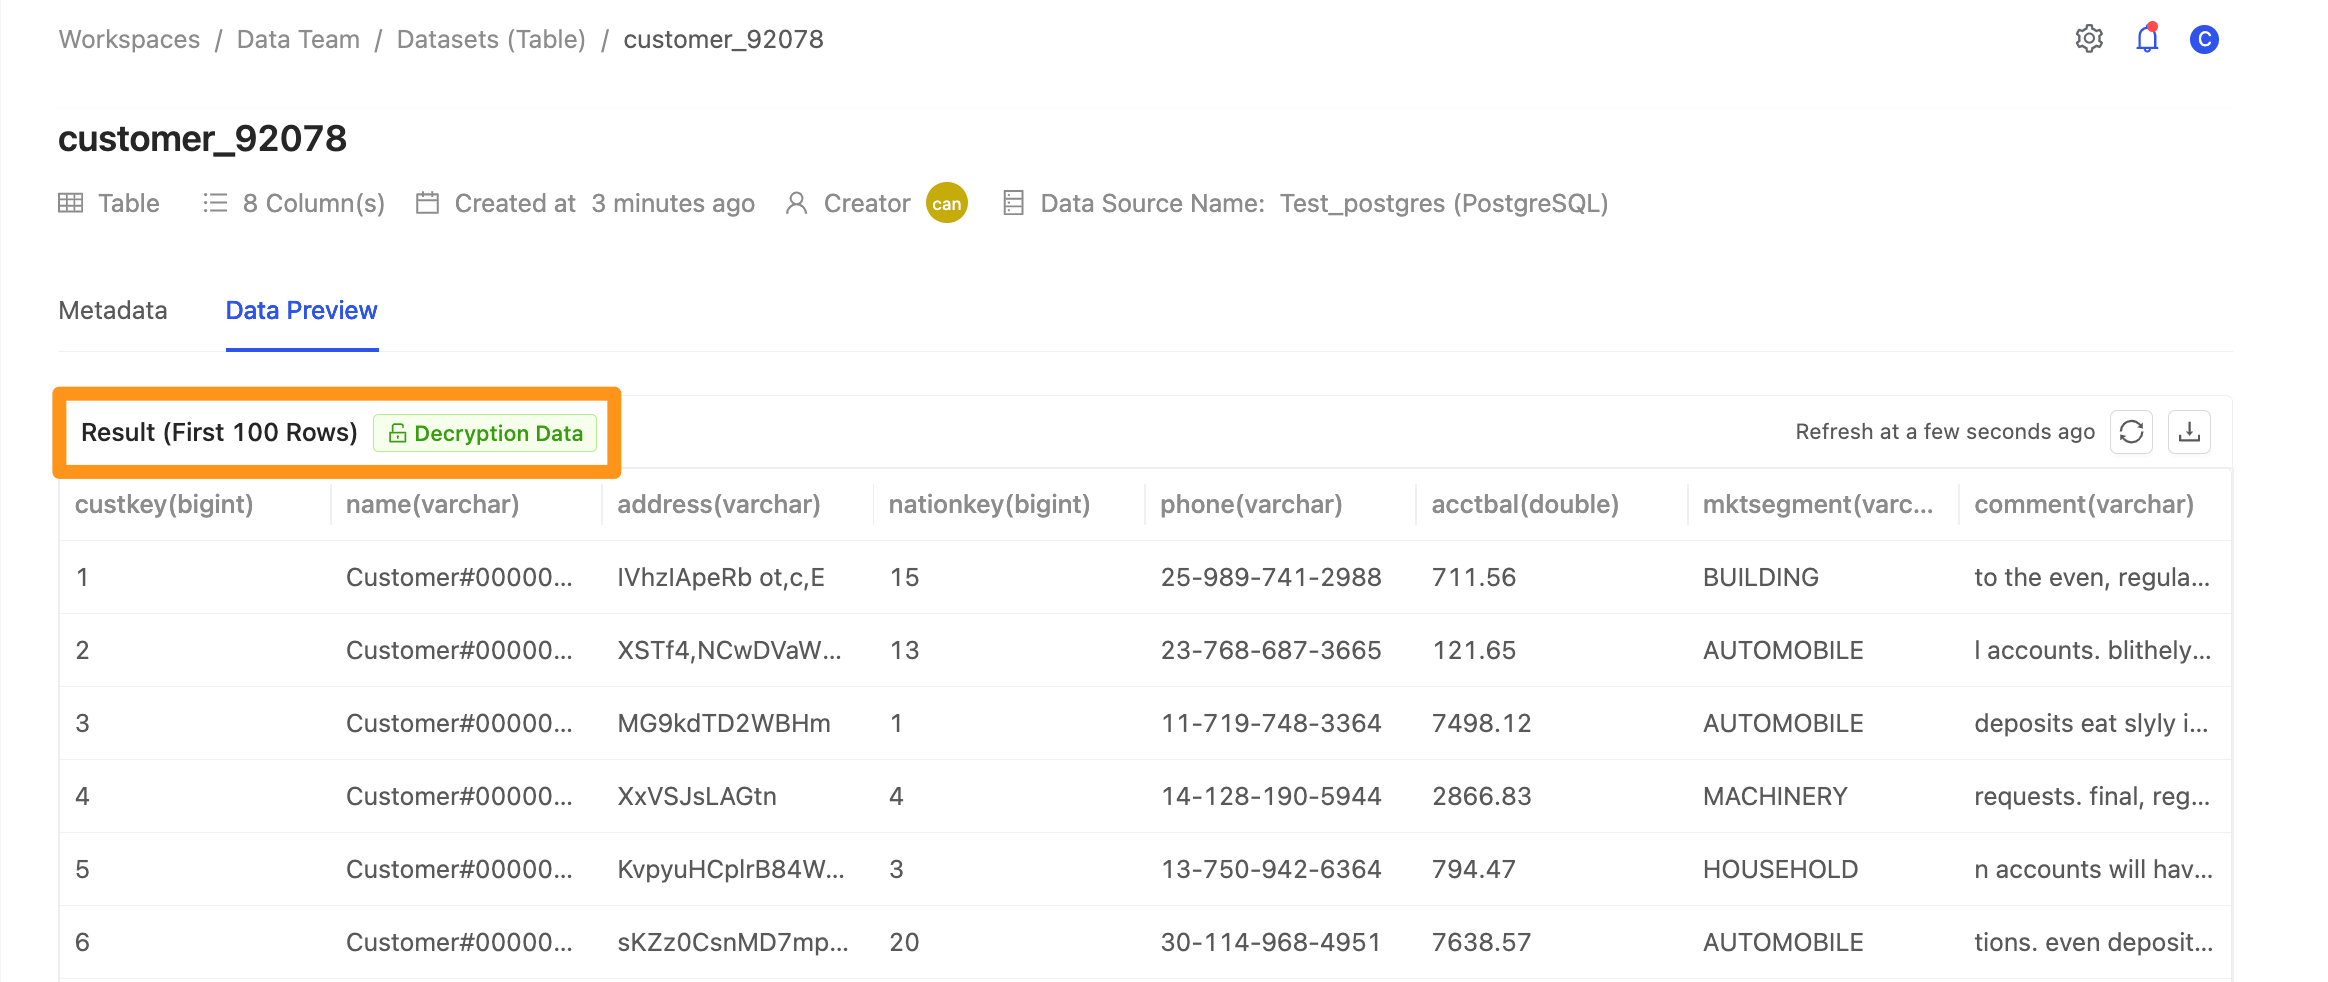
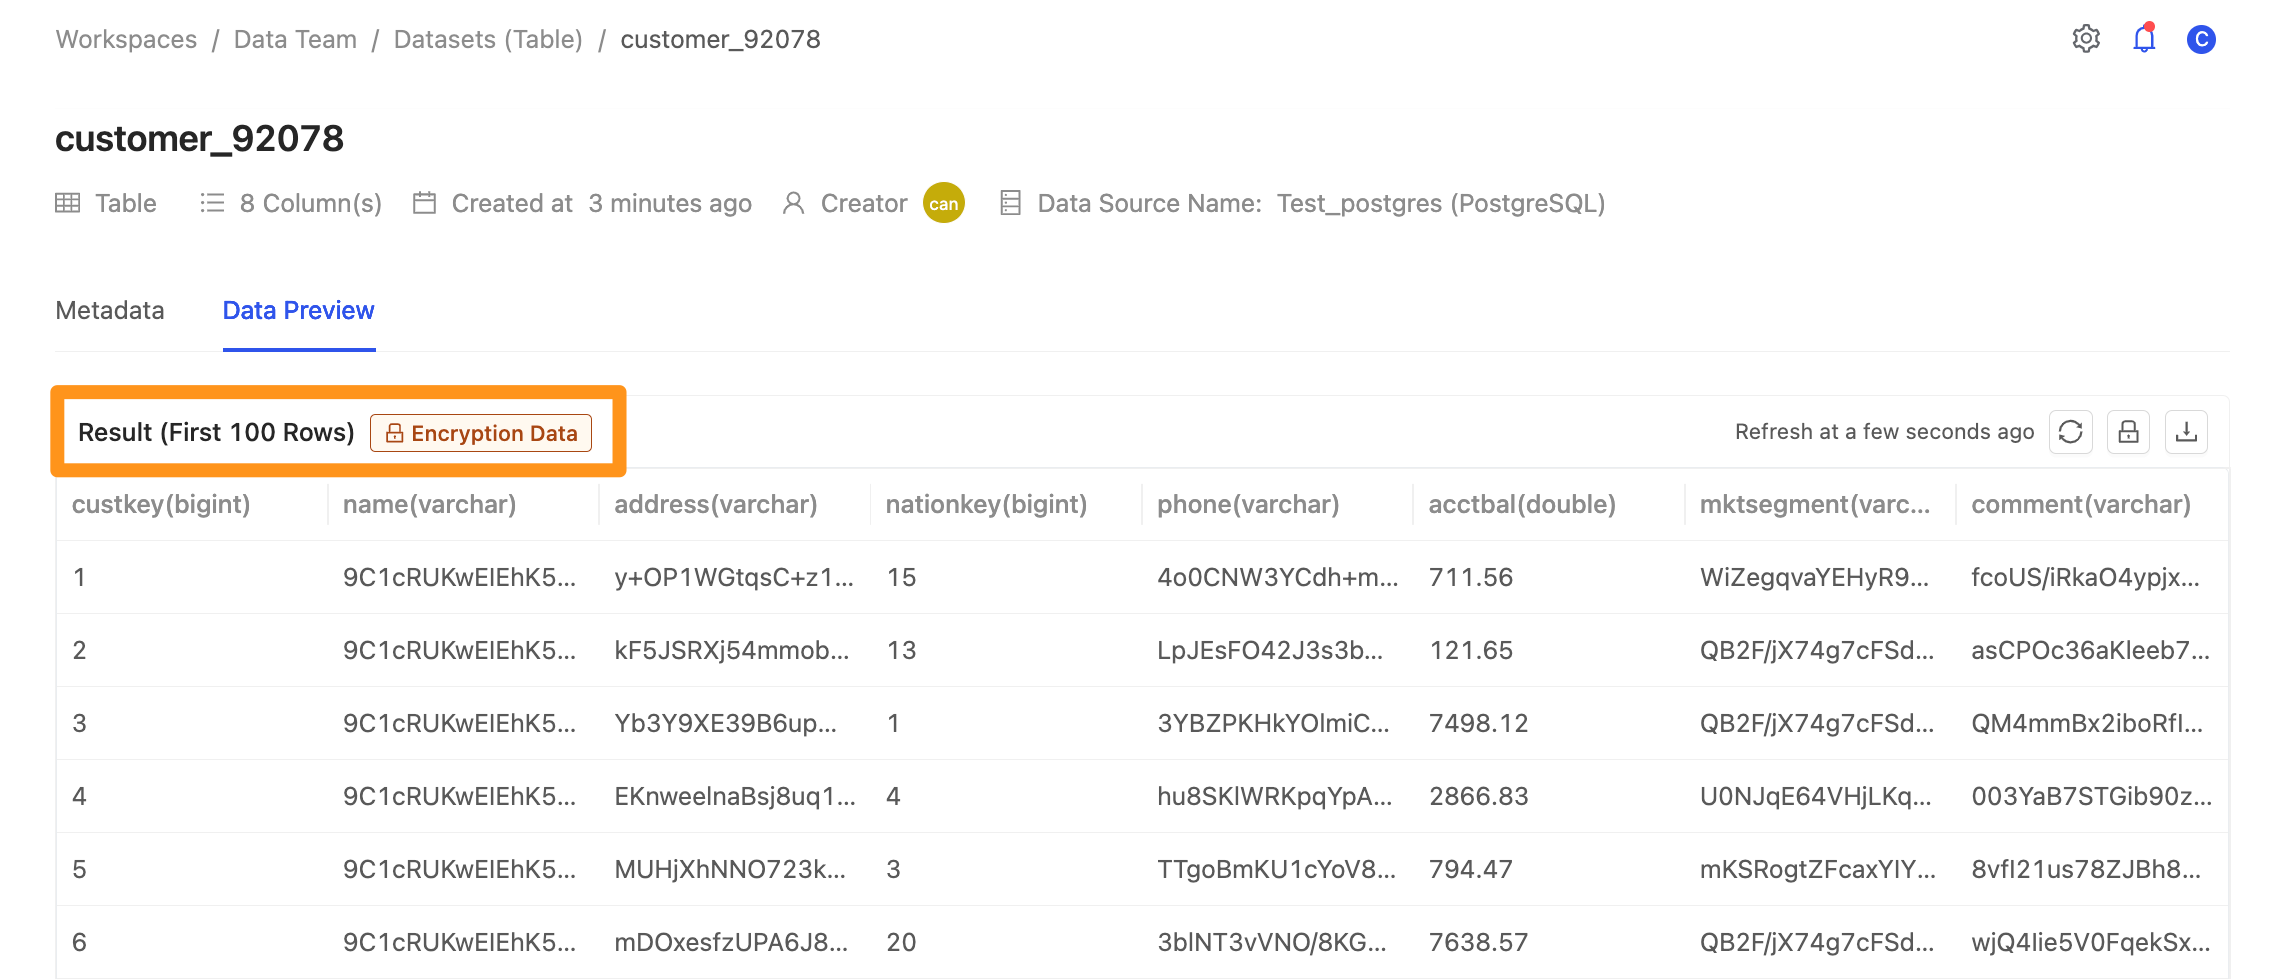
When the Data Policy applied to a dataset uses Encryption, users with decryption permission see an Encryption Data label on the data preview, meaning the data is currently encrypted.
Decryption permissions are configured by the Admin. See 2.8 System Administration & Settings: Data Policy.
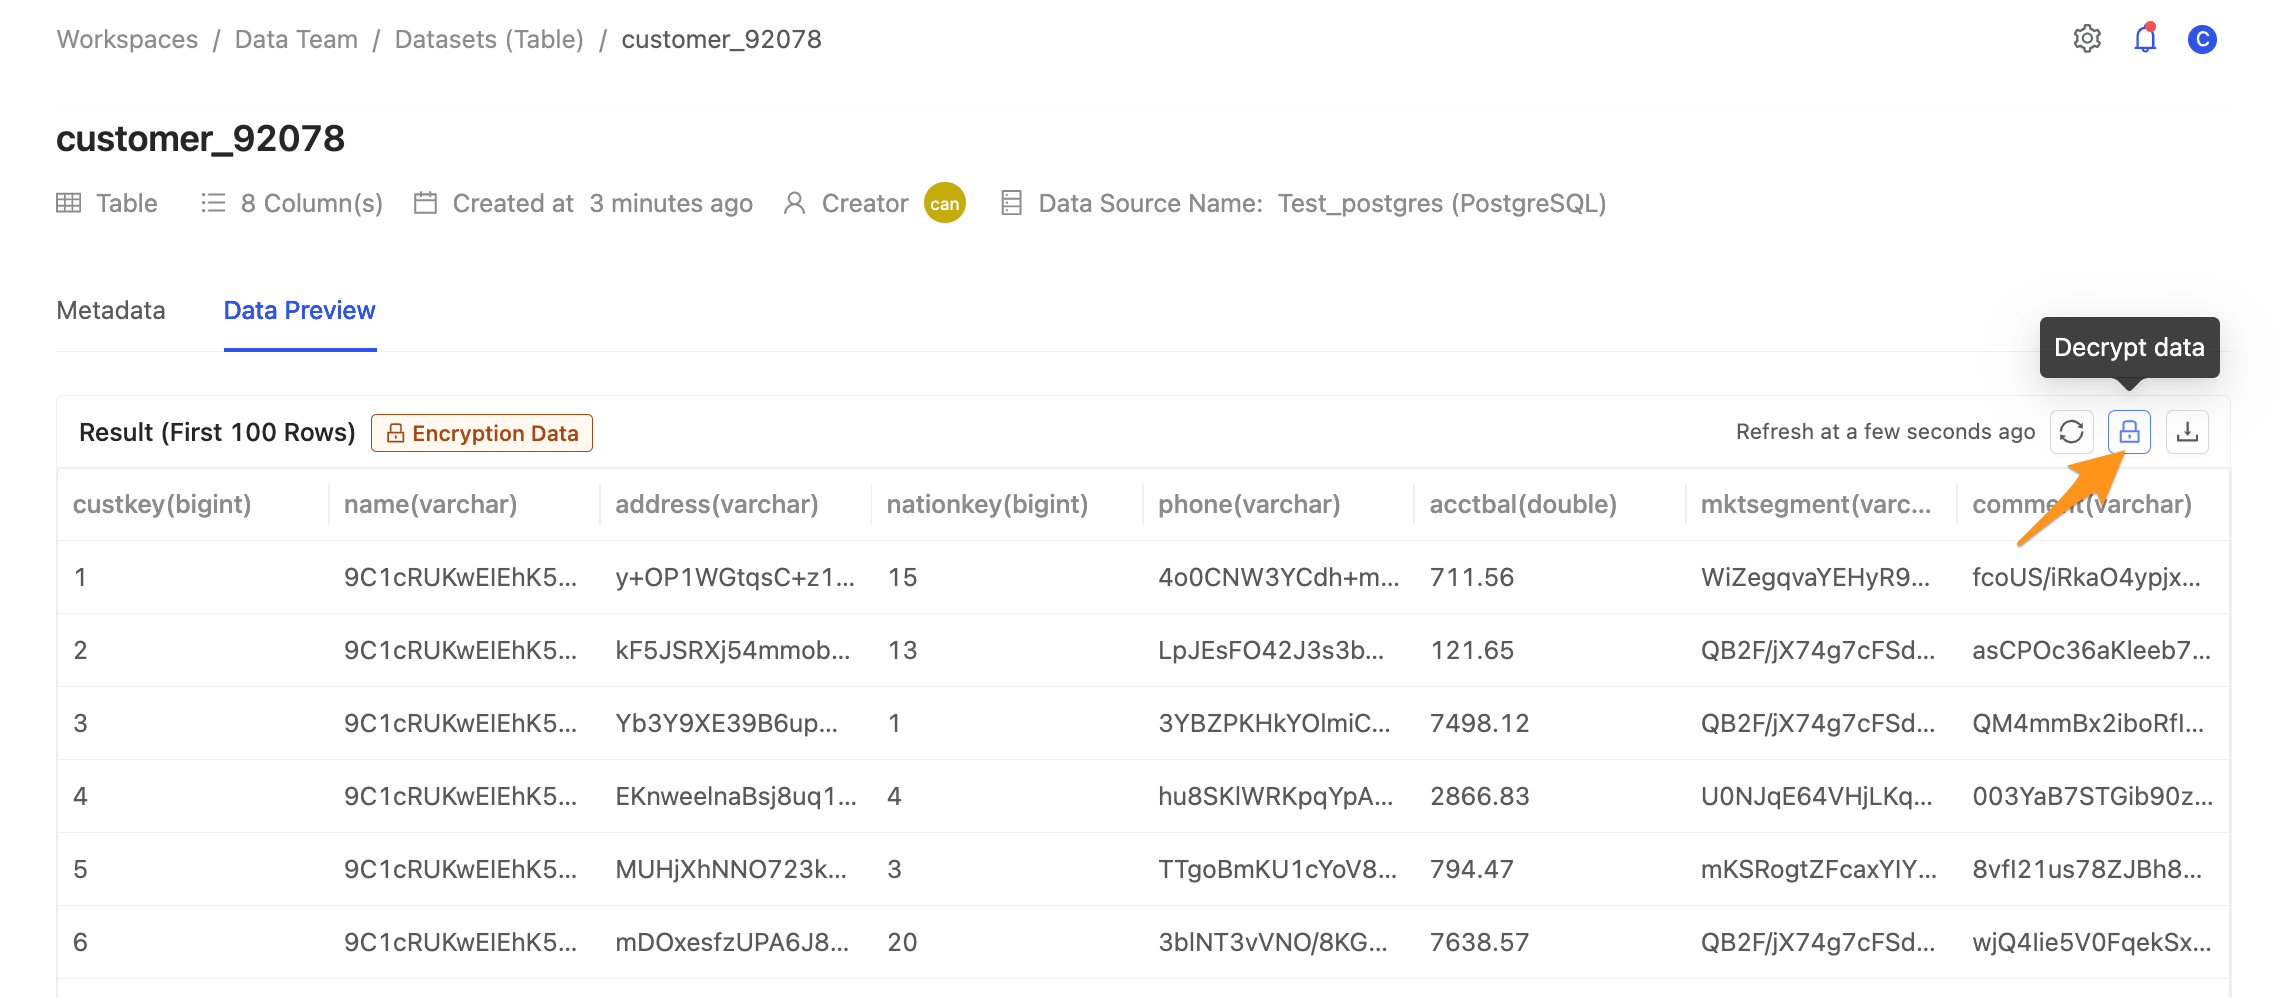
Click the lock icon, and the system decrypts the data automatically according to your decryption permissions.
After the data is decrypted, a Decryption Data label is shown, meaning the data is currently decrypted.