Data Policy
Data Policy is a privacy management tool that helps enterprises define unified data privacy and access control policies on the Canner platform.
Configure a Data Policy
A Data Policy must first be configured by the Admin, after which authorized users apply it to data sources and workspaces. This chapter describes how the Admin configures Data Policies on the Data Policies page. For the permissions and steps to apply Data Policies in data sources and workspaces, see Chapter 2.3 Data Catalog Module.
Up to 100 Data Policies are supported
Step 1: Open the Data Policies page
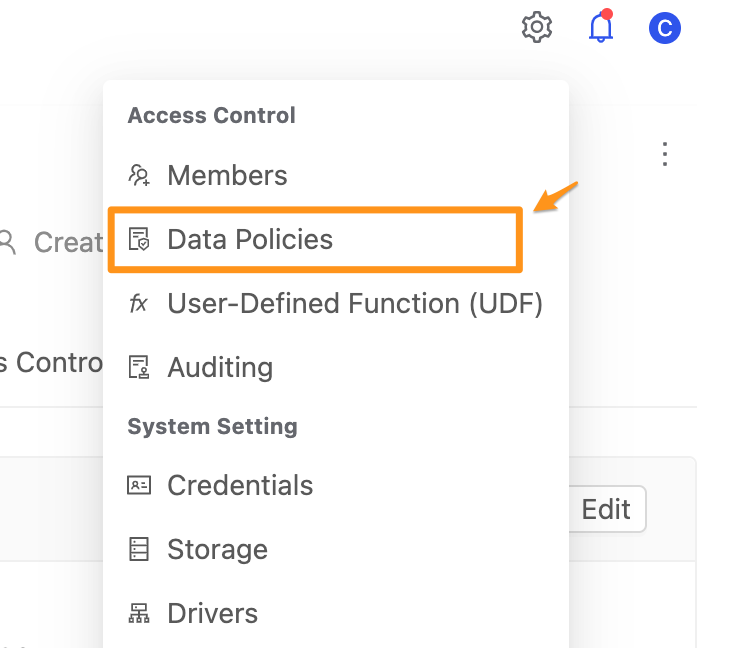
Click the settings icon in the upper-right corner and select Data Policies.
Data Policy permissions: only admin users can create Data Policies.
Step 2: Create a Data Policy
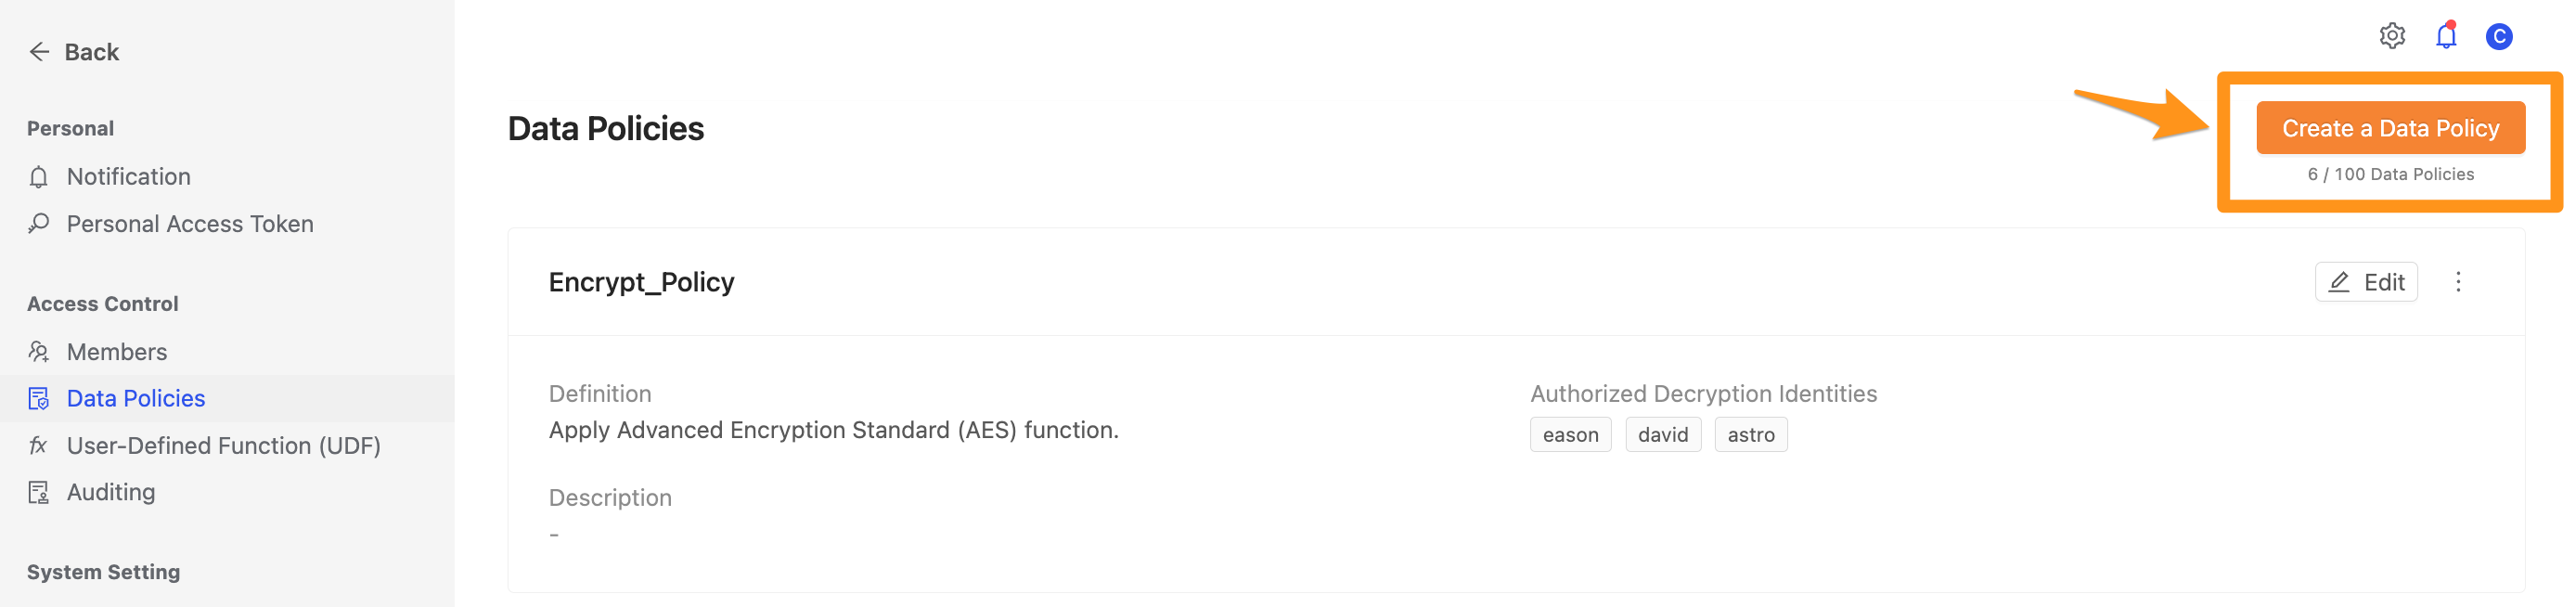
On the Data Policies page, click the Create a Data Policy button.
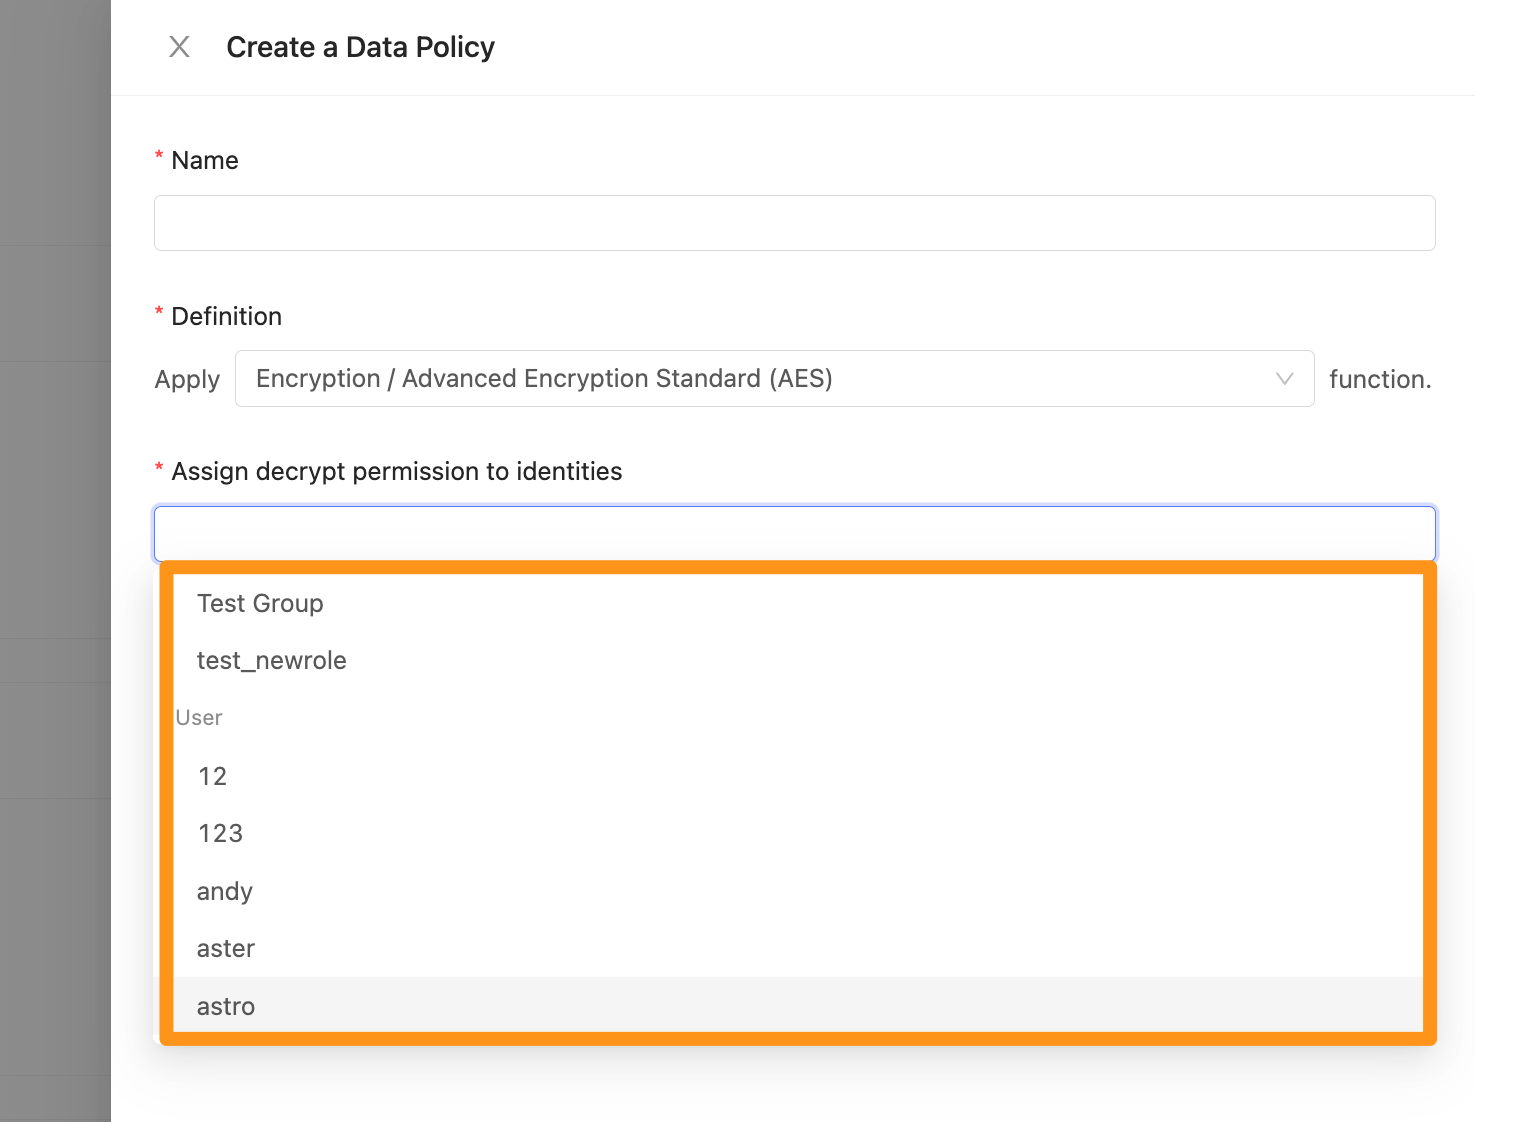
In the Create Policy dialog, configure the following:
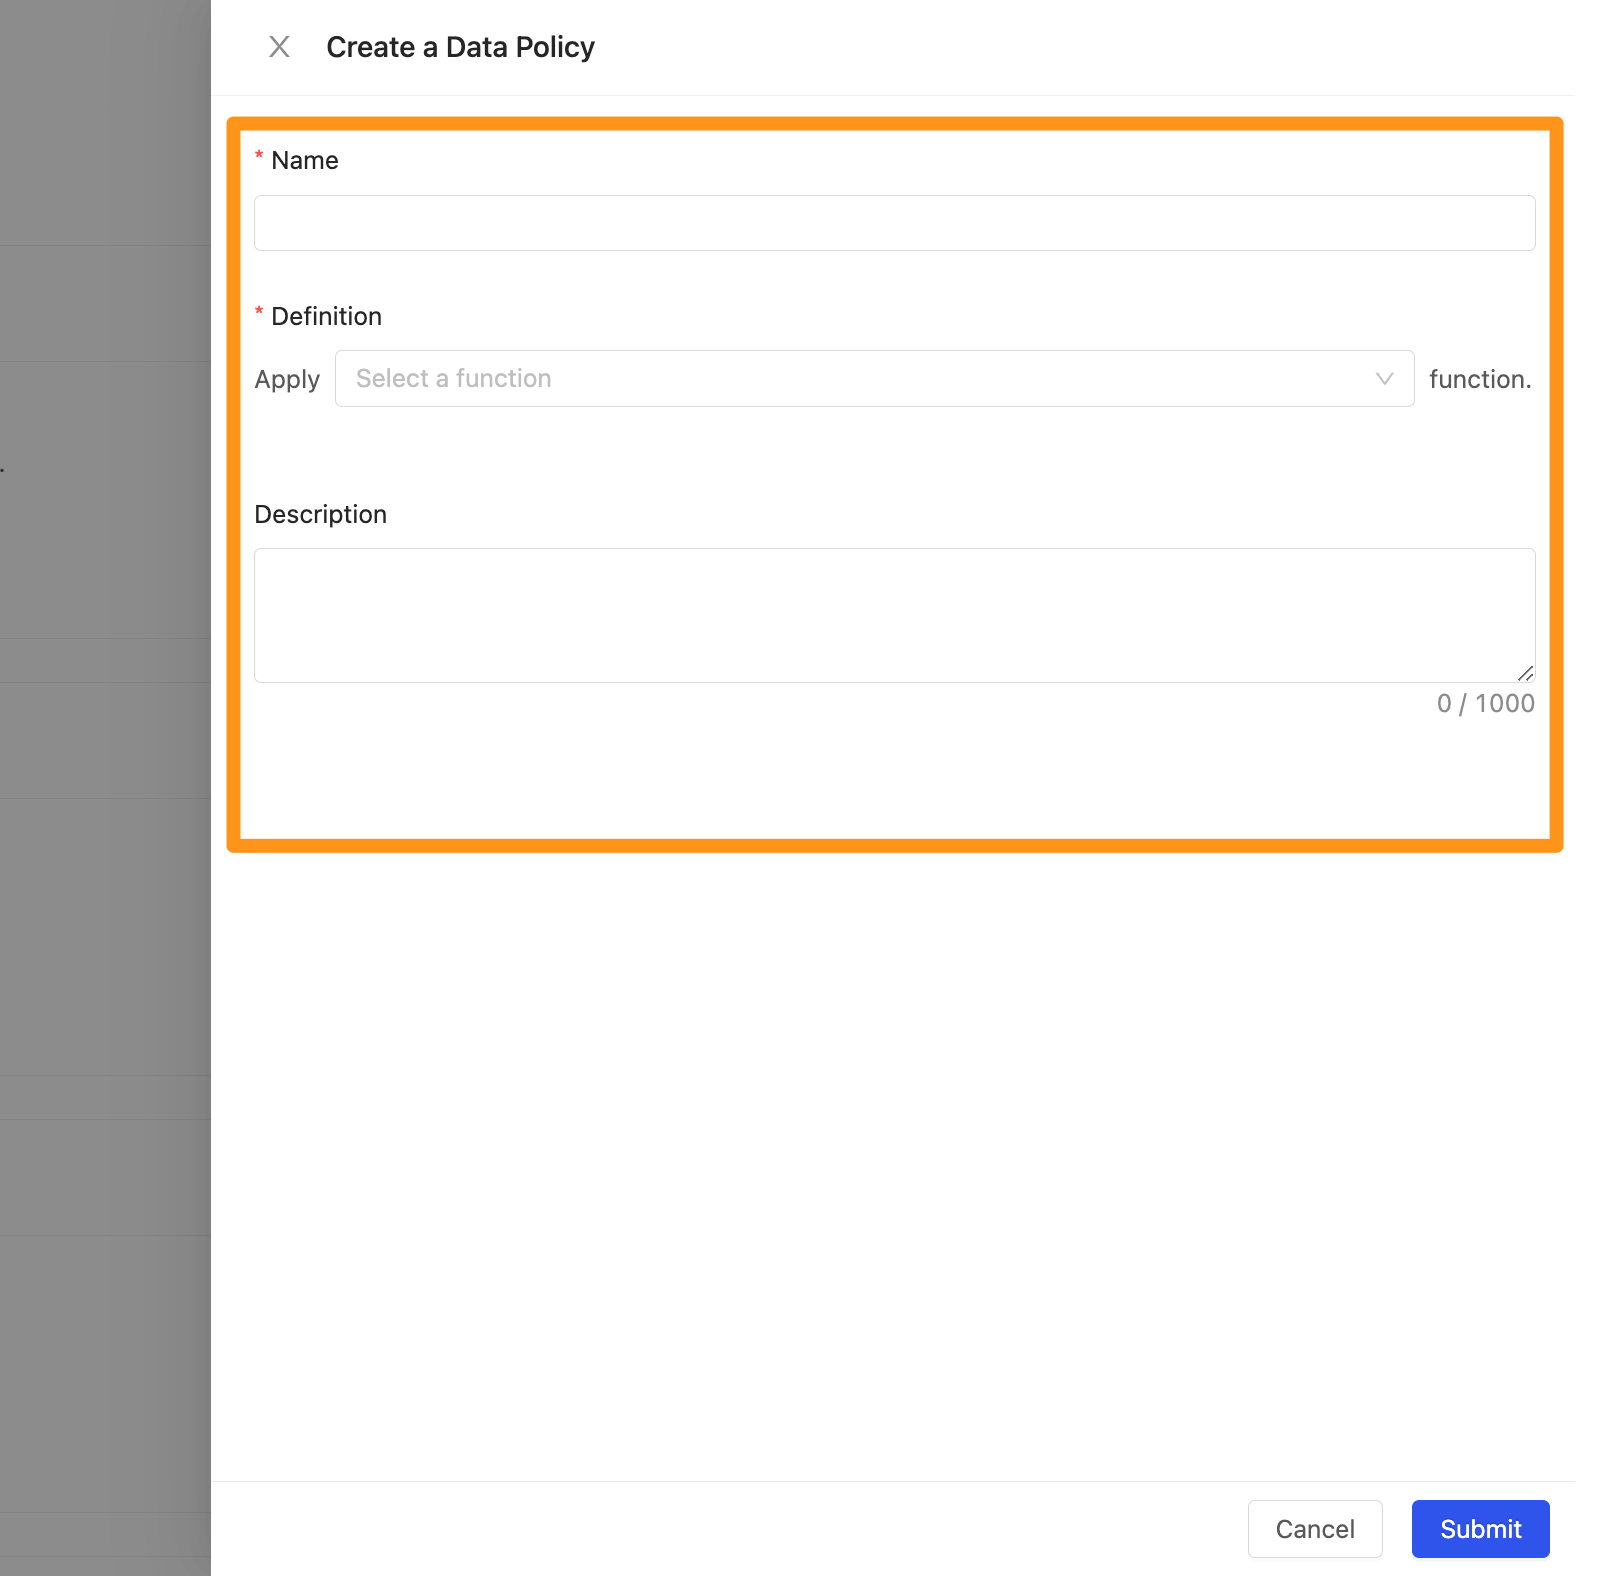
- Name: The display name of the policy; it can be changed
- Definition: The data protection method used by the policy
- Masking, Hashing, or Encryption
- Description: An optional description of the policy
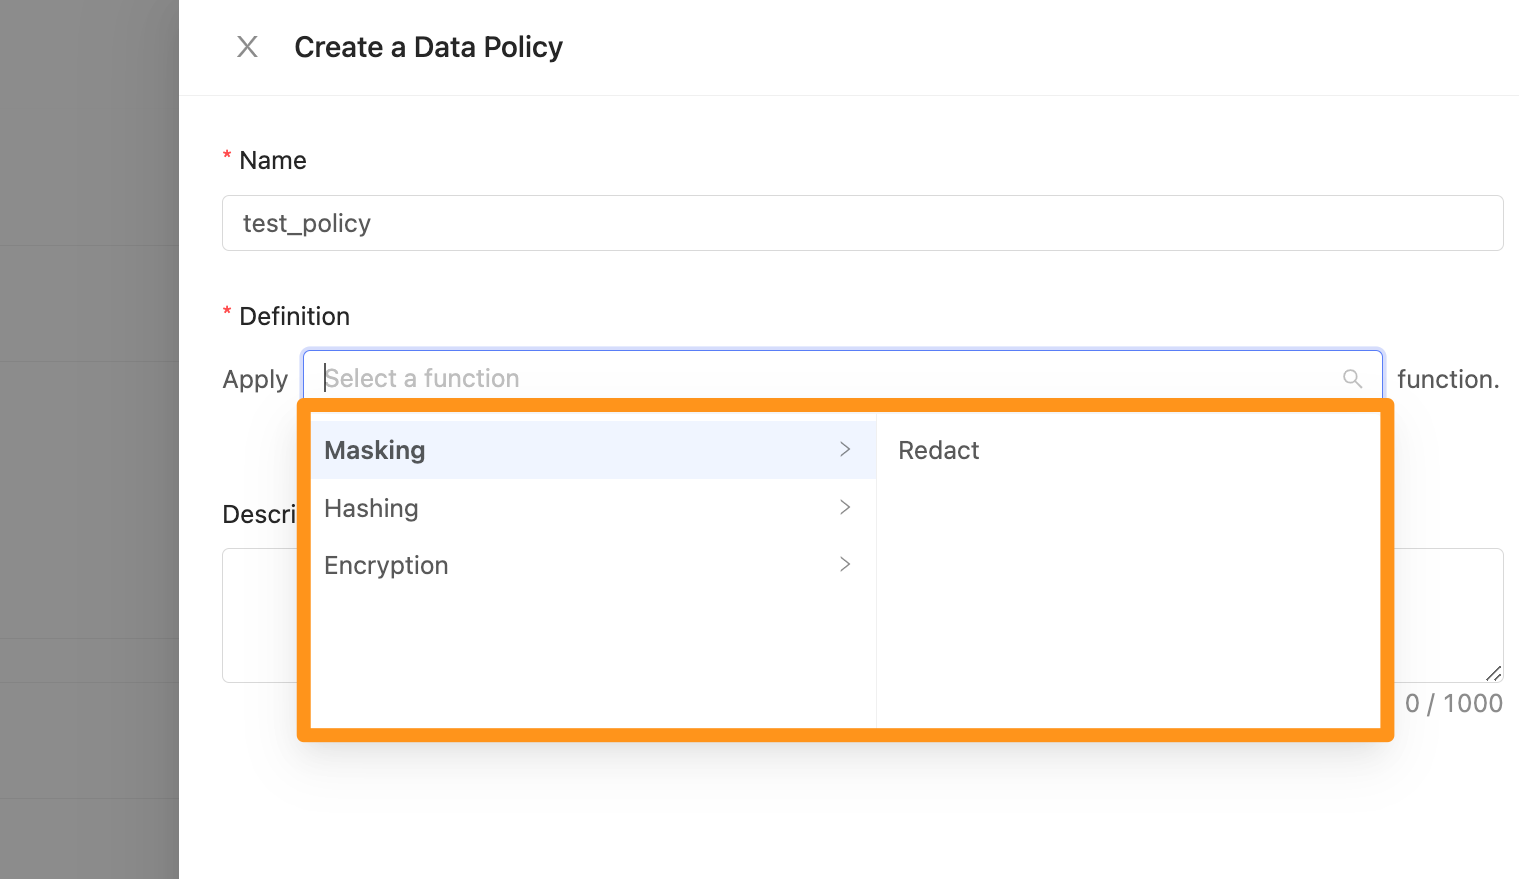
-
Masking
- Masking pattern: Built-in masking patterns for six types of personal data, including Email, Identification Number, Date of birth, Name, and Phone Number. Up to 2 patterns can be stacked. Note that stacked patterns are applied in order.
- Replace value with: The replacement value
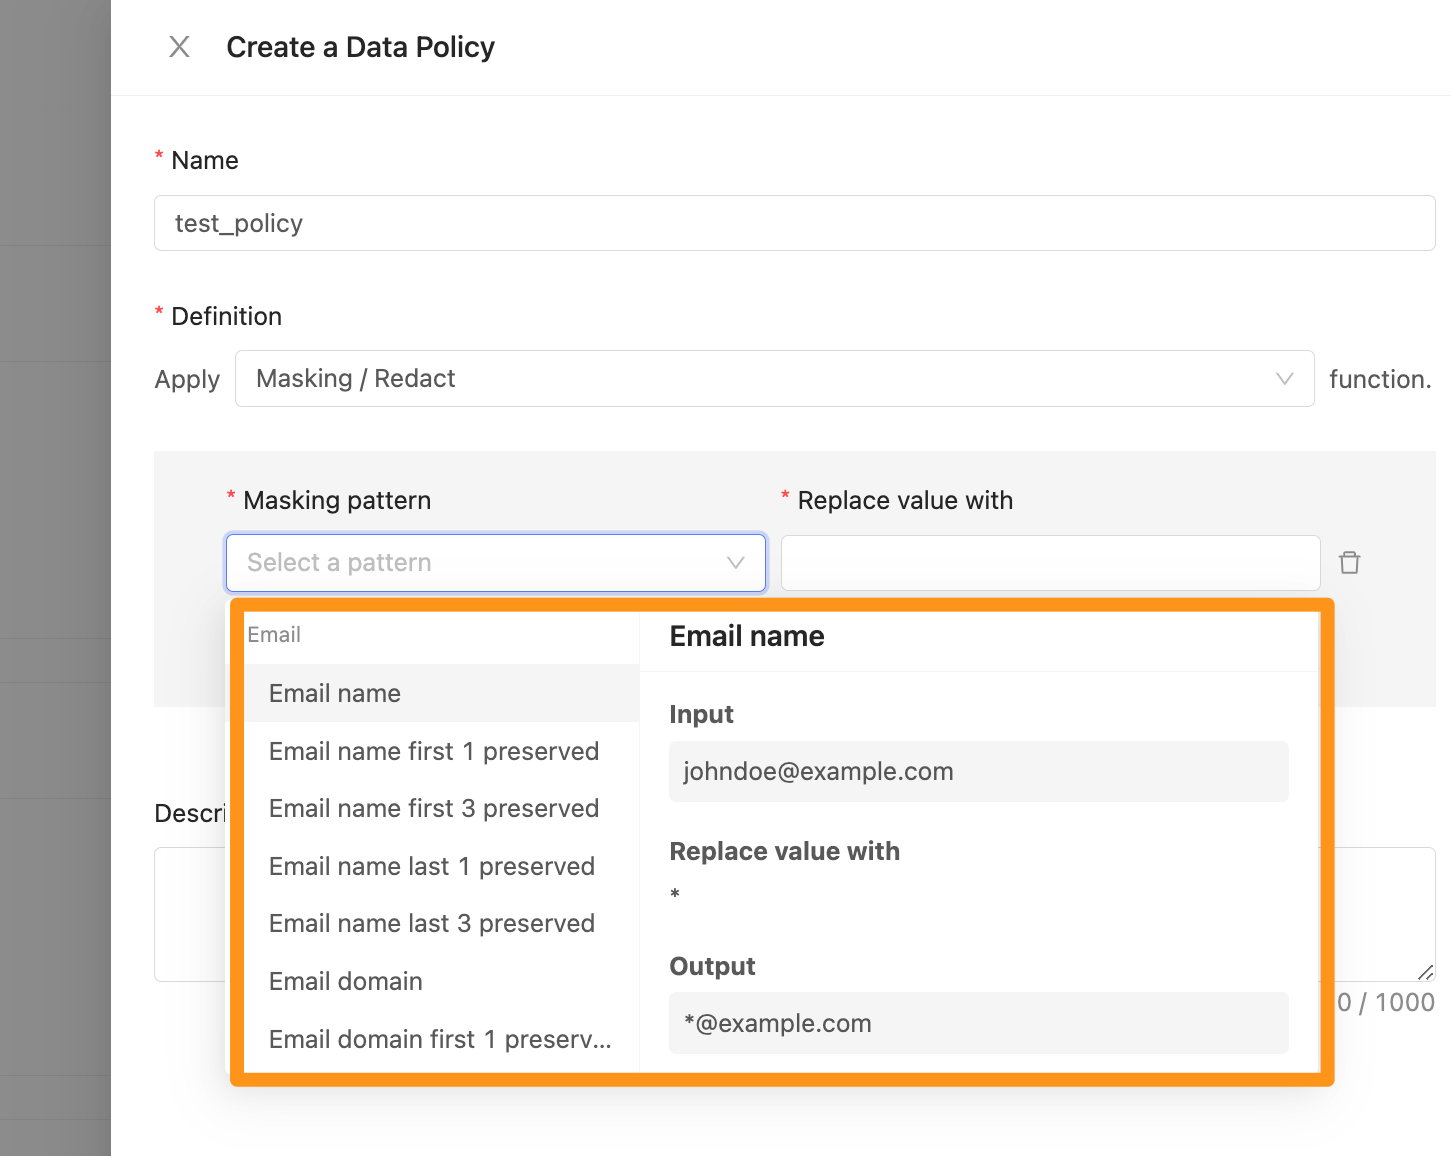
-
Hashing
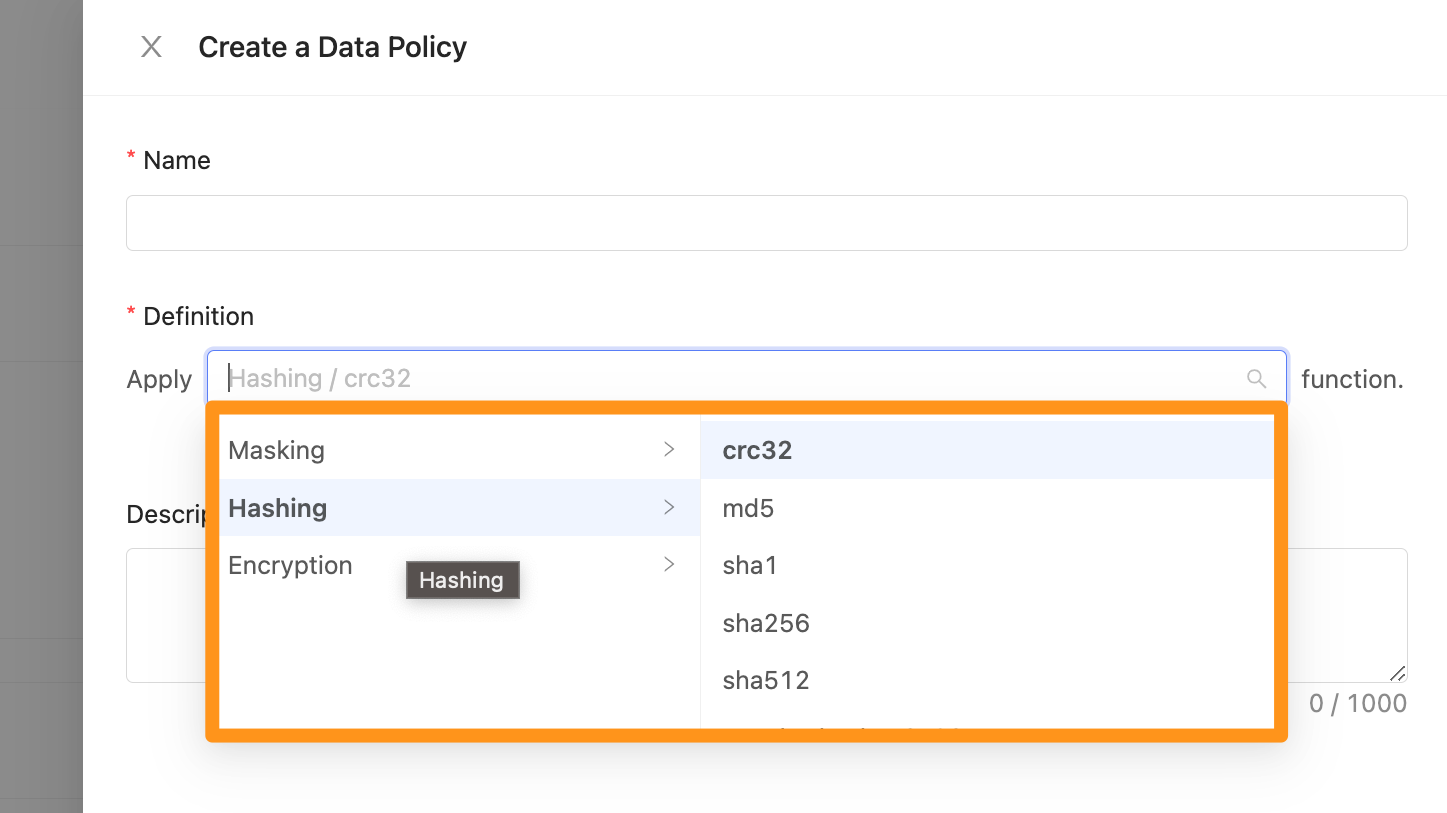
-
Encryption
Supports
AES,PBE, andRSAencryptionNotes on using RSAWith
RSAencryption, column values must be within 200 bytes; values over the limit fail to encrypt.RSAis also a strong encryption method, so encryption and decryption take longer, depending on the data length.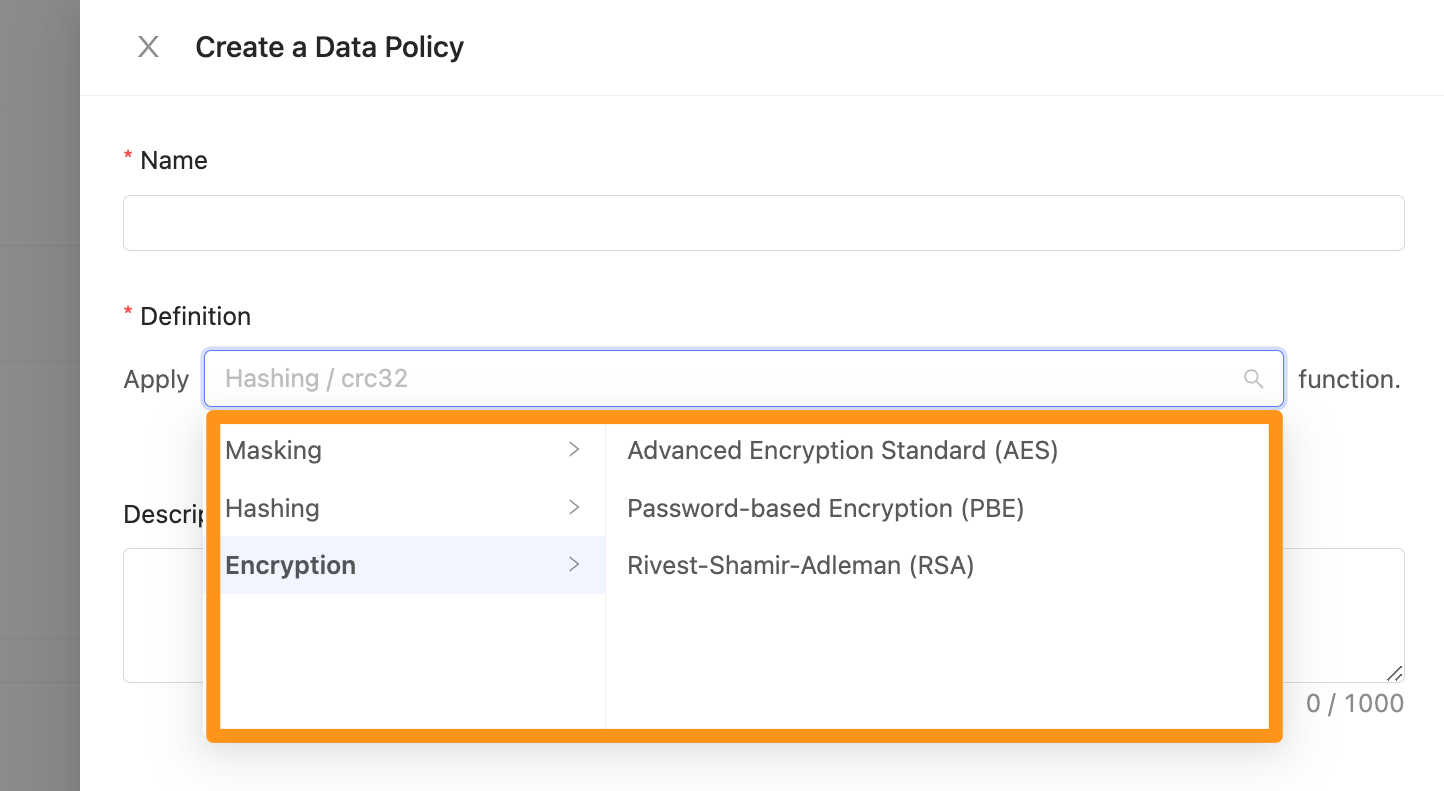
- Assign decrypt permission to identities: The groups and users allowed to decrypt. Note that the person who configures the Data Policy does not have decryption permission by default and must also be granted it to decrypt.
Step 3: Finish
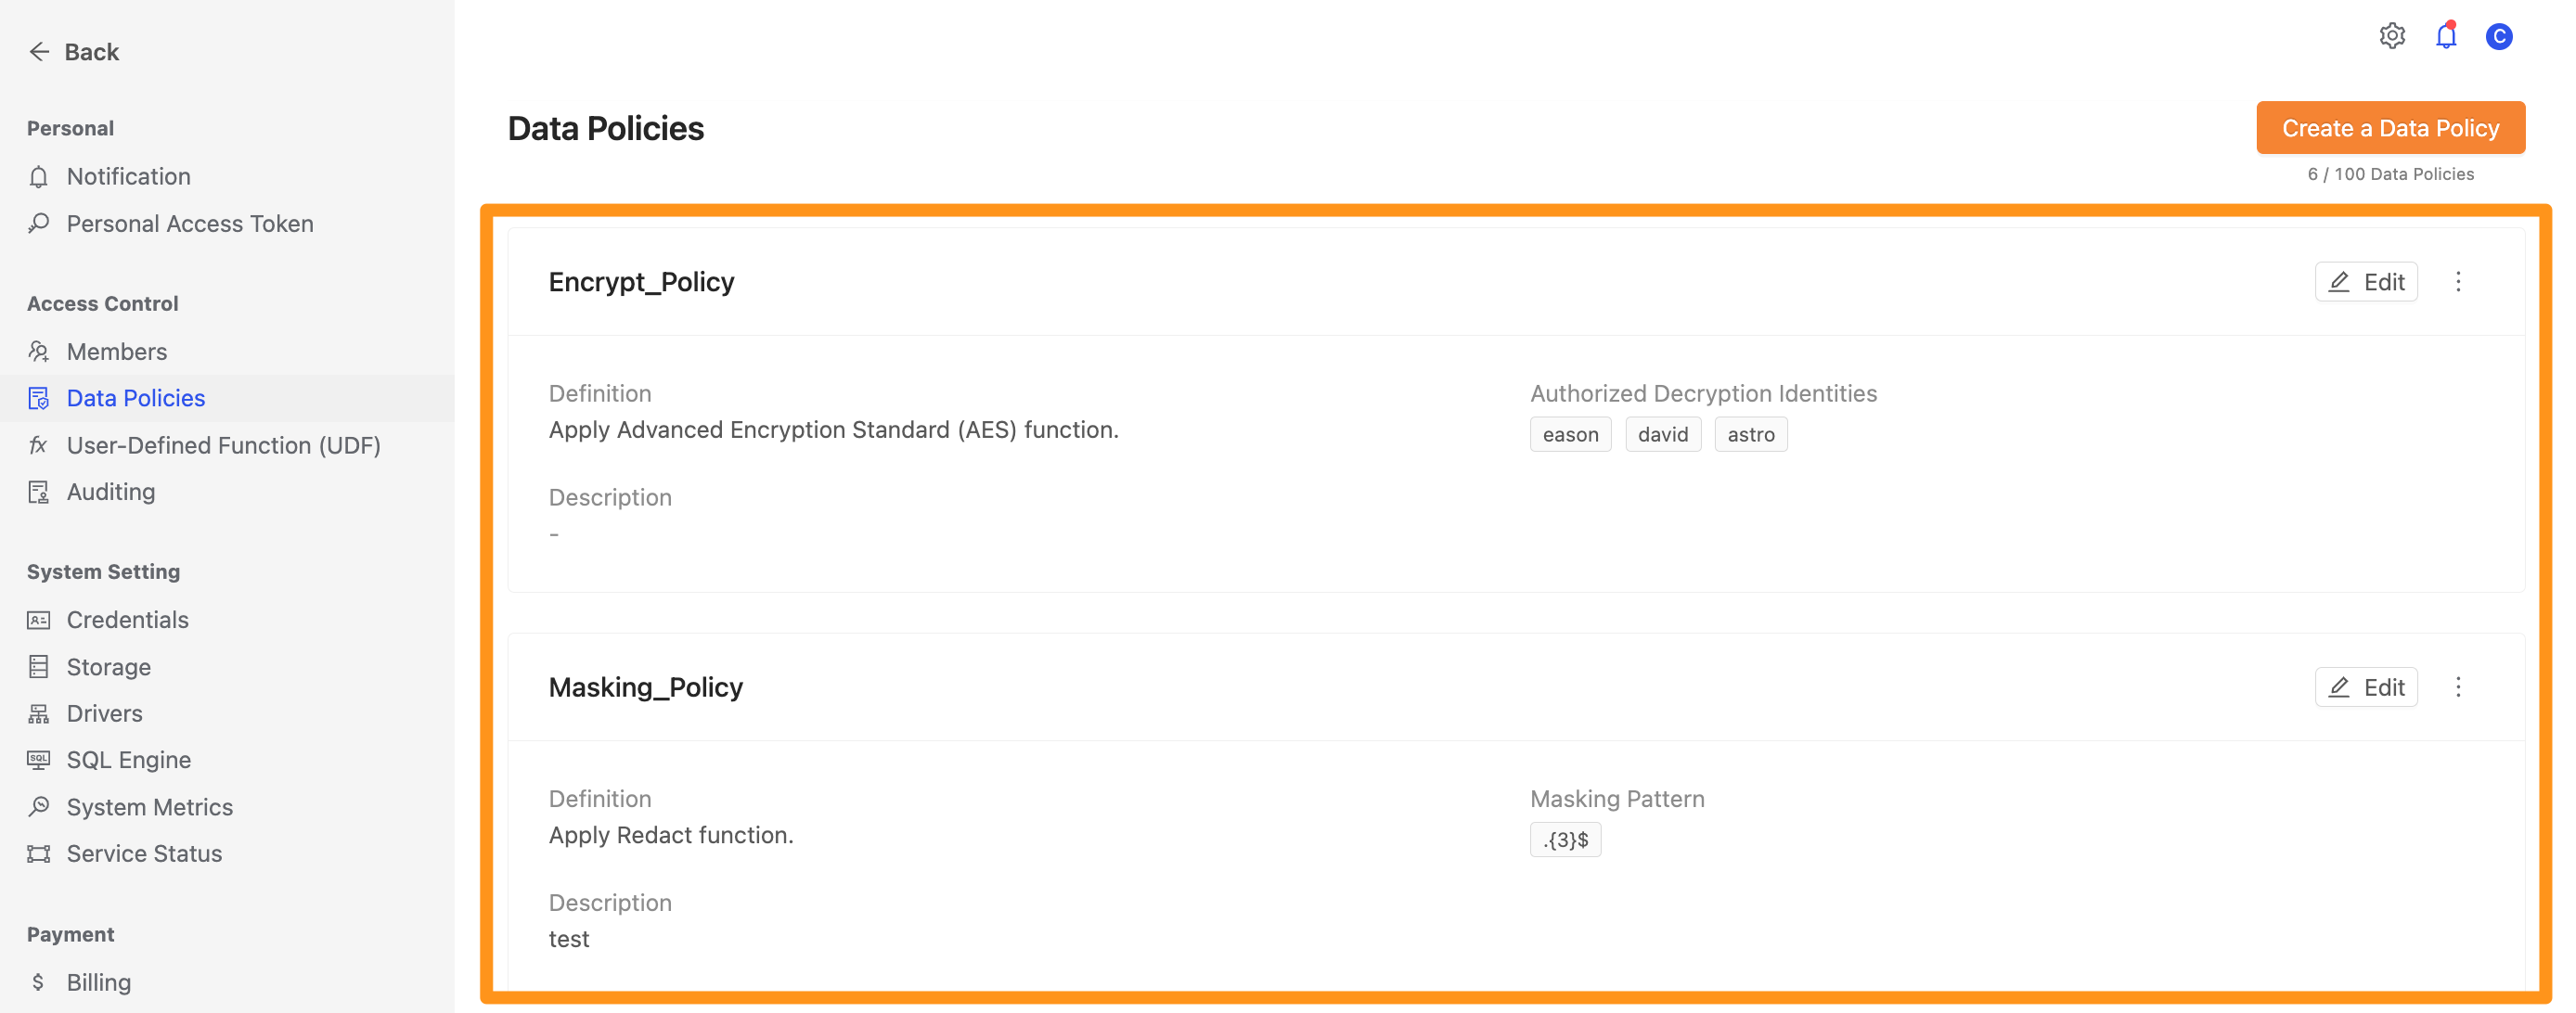
After you click Submit, all Data Policies created so far are listed.
Edit a Data Policy
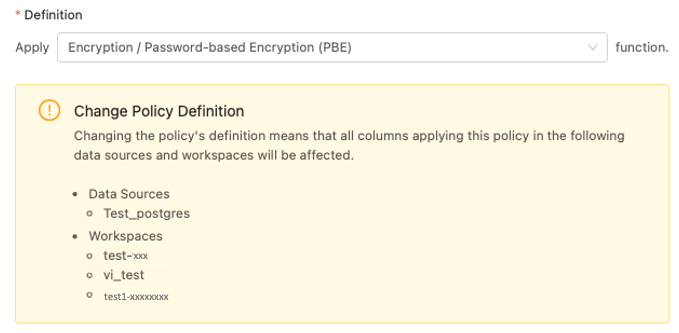
All fields of an existing Data Policy can be edited. If you change the masking/encryption method (the Definition field), the system warns you which data sources and workspaces the change may affect, as shown below.